
- SOC 2 Readiness
- 24/7 incident line
- 24/7 security operations team
Case studies
Client work and how we deliver it.
Browse the full library
Library entries by category
- Delivered case studies
- 3
- Partnership and platform stories
- 4
- Scoping briefs
- 17
- Planning examples
- 5
Showing 6 of 29 entries
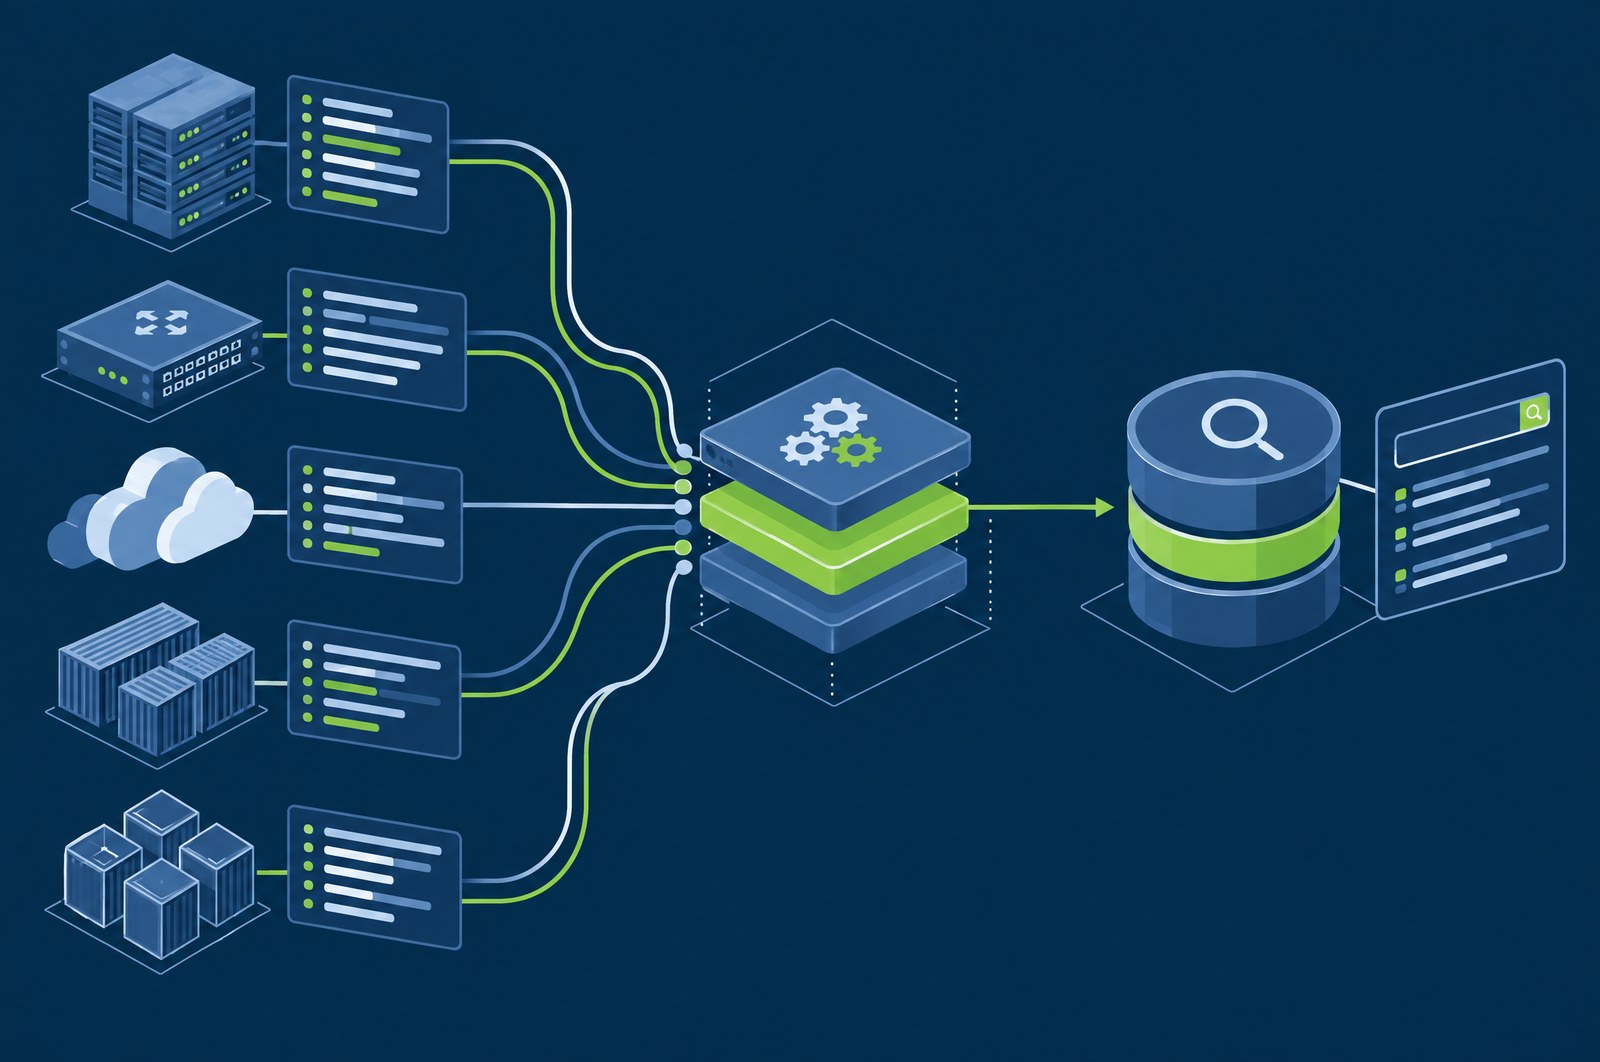
How to read this library
Evidence you can check, written the way the work was done
A case study is only useful to a buyer if it shows how a provider thinks. Each entry here sets out the situation the organization was in, what GuardsArm did or proposed, and what came out of it, in plain language and without inflated numbers.
Delivered case studies name the client and describe findings by count and theme. Scoping briefs show how an engagement was shaped before work began, including the questions worth putting to any provider. Partnership stories explain how GuardsArm works with resellers, colleges and other security firms. Planning examples walk through how a typical program is structured.
Every entry is available as a designed PDF for sharing with leadership, procurement or an audit committee. If you want to talk to the people behind a particular engagement, ask for them by name when you request a risk review.
What the published work covers
Penetration testing
External, application, API and segmentation tests, including retests that confirm each fix.
Detection and response
Around-the-clock monitoring, live detection demonstrations and analyst training programs.
Compliance readiness
SOC 2, PCI DSS, TISAX and health privacy law preparation for small and mid-size teams.
Security leadership
Virtual CISO and fractional security officer work for organizations without one.
Public sector and education
Municipalities, colleges and public bodies working to tender and insurance requirements.
Partnerships
White-label testing and referral arrangements with resellers and security firms.
Related services and resources
Questions about our case studies
- Can I speak to a reference client?
- Where a client has agreed to act as a reference we can arrange an introduction during a sales conversation. Ask when you request a risk review.
- Why do some entries not name the organization?
- Most security work is confidential. An organization is named only when it has agreed to be. Others are described by sector and size.
- Why are findings described only by count and theme?
- Publishing hosts, addresses or vulnerability detail would put the client at risk. Counts, severities and themes show the shape of the work without exposing anyone.
- Can I download a case study?
- Yes. Each entry has a PDF version. Complete the short form on the page and the download starts immediately, with a copy sent to your email.
- Do you have work in my sector that is not listed?
- Possibly. Not every engagement can be published. Tell us your sector and what you need and we will share what we can under a non-disclosure agreement.