
100% self-hosted
The entire platform, including the AI, runs on your own servers or private cloud. Telemetry never leaves your perimeter.
A self-hosted, white-label SIEM + XDR + EDR platform with a built-in AI SOC Analyst that runs entirely on your own servers.
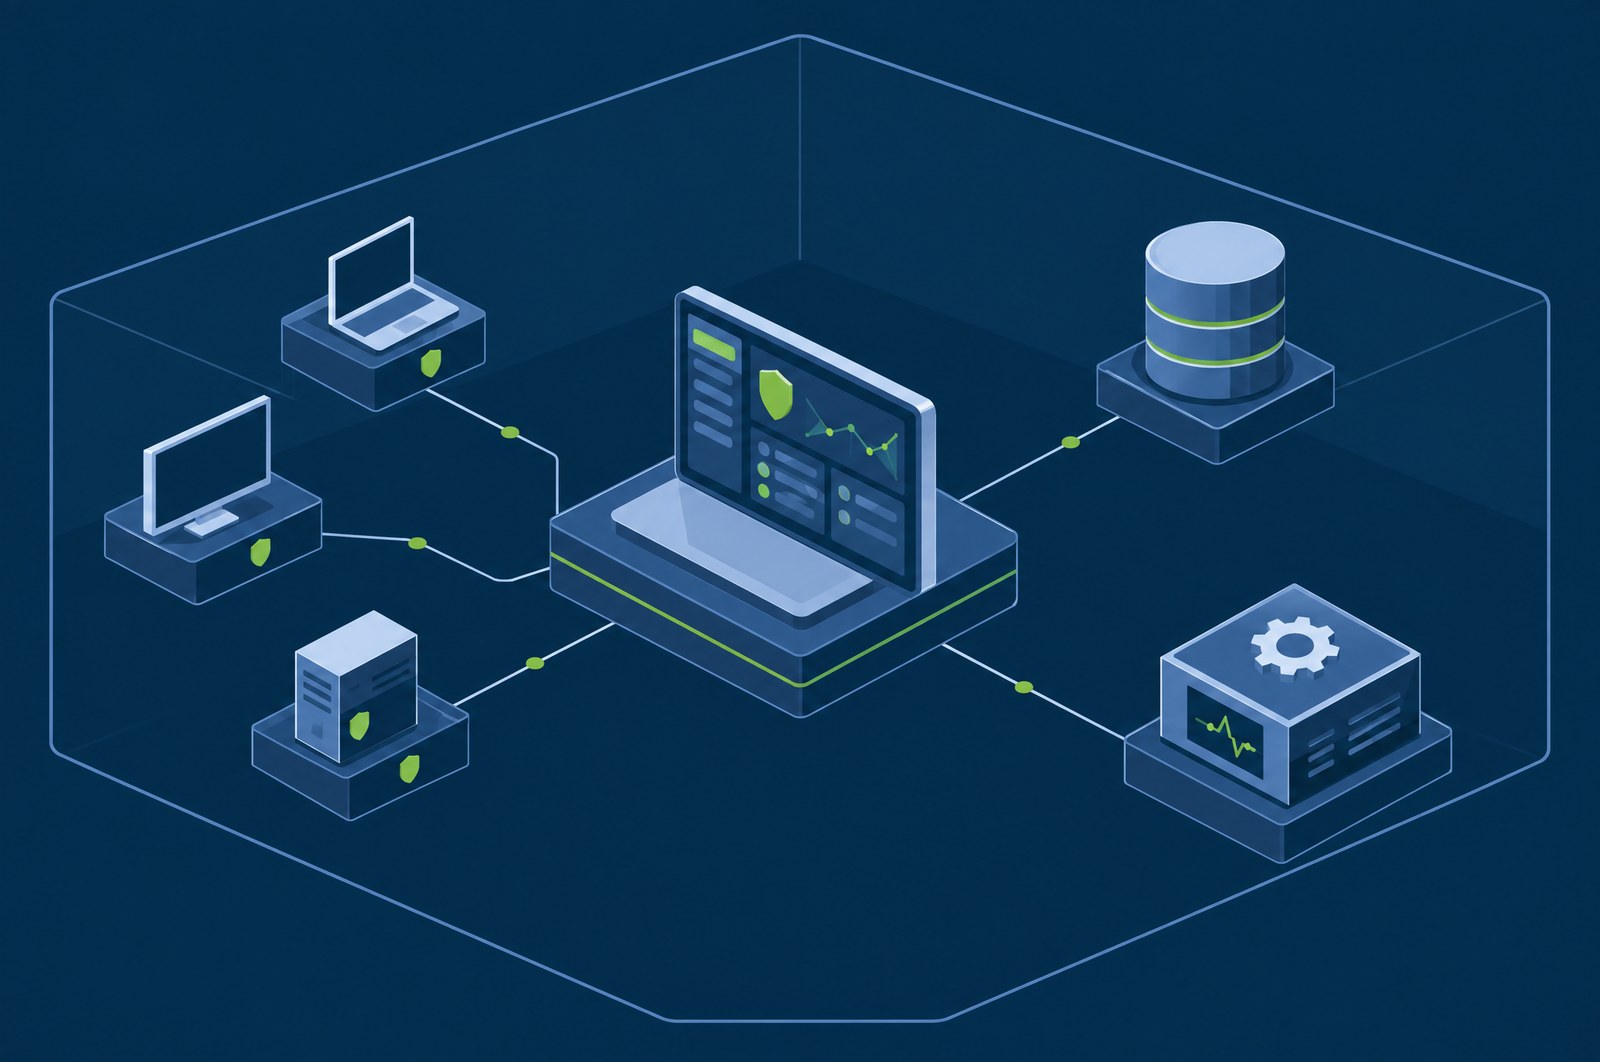
It unifies log management, endpoint detection and response, vulnerability management, threat intelligence, identity threat detection and security automation into one console — and adds an on-prem AI analyst that triages, correlates and explains alerts using a local language model, so sensitive security data never leaves your network.
Why it is different
Cloud MDR is the default model: your telemetry goes to someone else’s infrastructure, and their analysts and their AI look at it there.
GuardsArm inverts that. The entire platform — detection, storage, investigation and the AI analyst — runs on hardware you control. Auditable, no per-gigabyte metering, and no data leaving your perimeter to be analysed.
MSSPs and MSPs
Run one deployment, sell managed SOC to many clients, each fully isolated, and re-brand the console as your own.
Healthcare
On-premises means protected health information never leaves the network, with HIPAA compliance tagging and evidence built in.
Fintech and SaaS
SOC 2 and PCI evidence, a full audit log, RBAC and tenant isolation.
SMB and lean security teams
An AI SOC analyst that handles first-line triage, so a small team covers more ground.
Differentiators
The entire platform, including the AI, runs on your own servers or private cloud. Telemetry never leaves your perimeter.
The AI SOC Analyst runs a local language model. Full triage, correlation and reporting with zero data egress to an AI provider.
A fully re-brandable multi-tenant console. One deployment serves many customers, each isolated and seeing only their own data.
SIEM, XDR, EDR, vulnerability management, threat intelligence, ITDR, AIDR and SOAR in a single product — not a bundle of bolt-ons.
Detections and incidents map to ATT&CK techniques and tactics against a complete enterprise knowledge base.
Built on proven open foundations. No black box — you can audit the rules and the data, because both are yours.
Self-hosted licensing instead of per-gigabyte or per-event cloud metering.
Modules
Every module below shares the same telemetry, the same severity model and the same response engine. They are parts of one product rather than separately licensed tools stitched together.
Collect, normalise and search security events from your entire environment — on infrastructure you control.
ExploreTurn raw events into severity-graded, ATT&CK-mapped alerts — then connect them into real attacks.
ExploreDeep endpoint visibility and on-box response, from a lightweight native agent.
ExploreAn on-prem AI analyst that triages, correlates and explains — using a local LLM, so your data never leaves your network.
ExploreDetect identity-based attacks across your directories and cloud identities.
ExploreSecure your organization's use of GenAI and LLMs.
ExploreEnrich every detection with global threat context.
ExploreCatch malware three ways.
ExploreDeployment
On your own hardware, in your private cloud, fully air-gapped, or under your own brand. Security telemetry stays inside your perimeter in every one of them — including the AI analysis.
The entire platform runs on hardware you own, in a datacentre you choose. Nothing about detection, storage or analysis depends on a connection to us.
Deploy into your own cloud tenancy when you would rather not run metal. The boundary is still yours: your account, your region, your key management.
Dependencies are self-hosted, so the platform operates with no internet egress at all — including the AI. For classified and operational-technology environments this is the only workable model.
Service providers run one deployment across many customers, each isolated from the others, presented in a console carrying their own name rather than ours.
Purpose-built analyst models for triage, correlation and reporting, running a local language model on your own hardware. And it is a downstream consumer of detections, never the source of truth — so the platform keeps detecting whether or not the AI service is running.
Explore the AI SOC AnalystA walkthrough of the console, the deployment model, and what standing it up on your infrastructure actually involves.