FedRAMP Authorization: The Real Path for a SaaS Provider
Agency sponsorship, a 3PAO assessment and continuous monitoring forever. Whether the federal market is worth what authorization costs.
GuardsArm Team
Security Experts
FedRAMP is the most expensive compliance programme a SaaS company is likely to undertake, and the one with the clearest commercial justification: without it, you generally cannot sell to US federal agencies.
The decision is therefore commercial before it is technical. Is the federal market worth a programme measured in years and a permanent operational obligation afterwards?
Impact level sets the size
Authorization is sought at an impact level based on the sensitivity of the data your service will hold. The level determines how many NIST SP 800-53 controls apply, and the difference between levels is substantial.
| Level | Data sensitivity | Relative control count |
|---|---|---|
| Low | Limited adverse effect if compromised | Smallest set |
| Moderate | Serious adverse effect | The common target, and much larger |
| High | Severe or catastrophic effect | Largest, with the most demanding requirements |
Moderate is where most SaaS providers land, because most federal data that is not public falls there. Do not scope to High speculatively.
Sponsorship is the gating problem
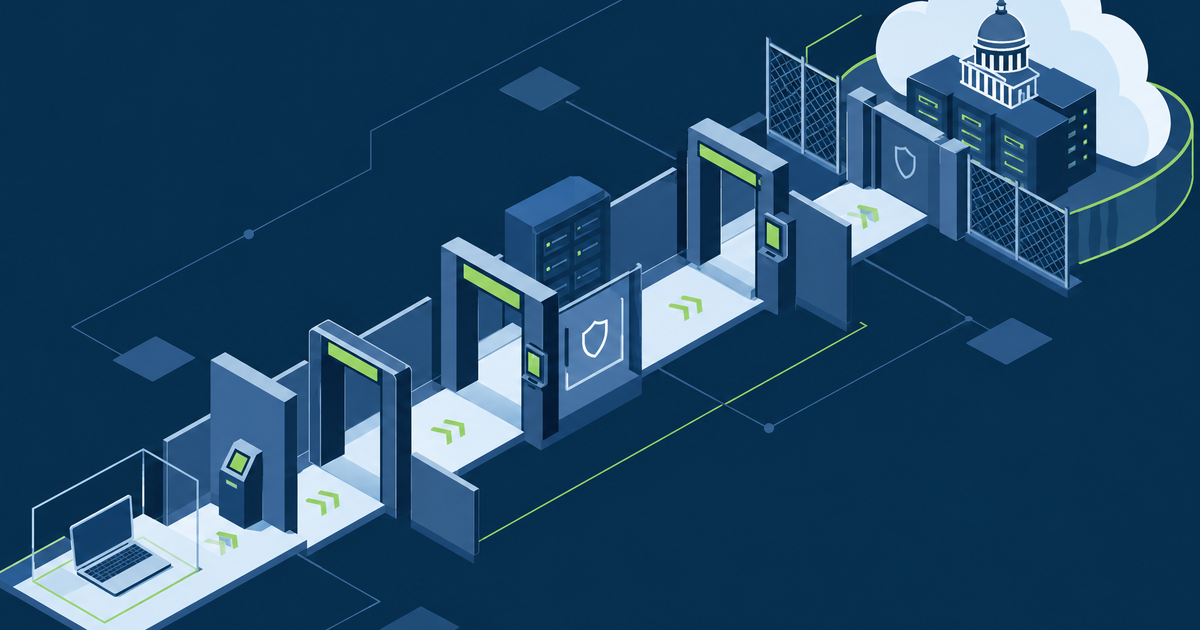
You cannot simply decide to become authorised. The routes require either an agency willing to sponsor you and issue an Authority to Operate, or authorization through the programme's own board process.
Agency sponsorship means finding an agency that wants your product enough to commit staff to reviewing your package. That is a sales problem as much as a compliance one, and it is where many programmes stall — a company spends heavily on readiness, then cannot find a sponsor.
Secure the sponsor relationship before the heavy spending, not after.
What the programme involves
- Readiness assessment, often producing a readiness report from a 3PAO
- System Security Plan describing the boundary and every control implementation — a very large document
- Control implementation, against the applicable 800-53 baseline
- 3PAO assessment — an accredited third-party organisation tests the controls and produces a Security Assessment Report
- Authorization decision by the sponsoring agency or board
- Continuous monitoring, indefinitely
Continuous monitoring is the part that surprises people
Authorization is not an event. Once authorised you owe ongoing obligations: monthly vulnerability scanning with defined remediation timeframes, monthly reporting, annual assessment of a subset of controls, and a significant change process that requires approval before you make architectural changes.
That last item is the one engineering teams find hardest. A SaaS company used to shipping continuously discovers that some changes to an authorised boundary require a review process before deployment.
Budget permanent staff for continuous monitoring. Organisations that treat authorization as a project and disband the team afterwards fall out of compliance within a year.
Reducing the cost
- Inherit from your infrastructure provider. Major cloud providers hold their own authorizations, and you inherit a substantial share of infrastructure controls. Document the inheritance carefully — it is a large part of the package.
- Define a tight boundary. Only what is in the authorization boundary is assessed. Keep corporate IT outside it.
- Reuse an authorization. A service authorised for one agency can be reused by others, which is the return on the investment.
- Do not scope to High unless the data genuinely requires it.
See cloud compliance for how the inheritance argument is made, and NIST 800-53 tailoring for the underlying control catalogue.
Where to start
Answer the commercial question first with real numbers: which agencies, what contract value, over what period. A programme of this size needs a business case, and building one after the spending has started is how companies end up authorised for a market they cannot actually sell into.
Engineering changes you should expect
FedRAMP reshapes how a SaaS product is built and operated, not just how it is documented:
- A separate government environment is common, isolated from your commercial estate, with its own deployment pipeline and its own staff access model
- Personnel requirements — some roles require screened US persons, which affects hiring and support rotas
- FIPS-validated cryptography rather than merely strong cryptography
- Vulnerability remediation deadlines by severity, enforced through monthly reporting rather than left to your own prioritisation
- Change control on the authorised boundary, which slows some deployments
The staffing implication is usually the one that surprises founders. A government environment with restricted personnel access needs people who can work in it, and that is a recruitment constraint as much as a technical one.
StateRAMP and the smaller variants
If your buyers are state and local government rather than federal, StateRAMP and similar state programmes may be the relevant path, and several accept or reuse FedRAMP work. Confirm which programme your actual pipeline requires before defaulting to the federal one — it is a substantially smaller undertaking for a market that may be equally valuable to you.
GuardsArm supports FedRAMP readiness and boundary design. See FedRAMP compliance or book a scoping call.
Written by GuardsArm Team
Our team of cybersecurity experts brings decades of combined experience in penetration testing, compliance auditing, and incident response. We're dedicated to helping organizations strengthen their security posture.
Take the next step on “FedRAMP Authorization: The Real Path for a SaaS Provider”
Talk to the GuardsArm team about how these services apply to your environment.