Immutable Backups for Hospitals: The Only Ransomware Insurance That Works
Modern ransomware finds and destroys backups before deploying the payload. Immutability is the property that makes a copy survive an attacker who holds your domain admin credentials.
GuardsArm Team
Security Experts
Ransomware operators learned years ago that encrypting production is not enough if the victim can restore. So the modern sequence is: gain access, escalate to domain administrator, find the backup infrastructure, destroy or encrypt every copy, then deploy the payload. By the time the ransom note appears, recovery has already been removed as an option.
Immutability is the property that breaks that sequence.
The test that matters
Forget product categories and ask one question of every copy of your data:
If an attacker held domain administrator credentials for four hours, could they destroy this?
If yes, it is availability infrastructure. It protects against hardware failure and human error, both of which are real — but it is not ransomware recovery.
How immutability is implemented
| Mechanism | Where | Note |
|---|---|---|
| Object lock (S3 and compatible) | Cloud or on-prem object storage | Compliance mode cannot be shortened even by the account root |
| WORM on purpose-built appliances | Dedicated backup appliances | Vendor-enforced retention lock |
| Tape | Offline media | Genuinely air-gapped once ejected; slow to restore |
| Immutable snapshots | Some storage arrays | Verify the admin cannot shorten retention |
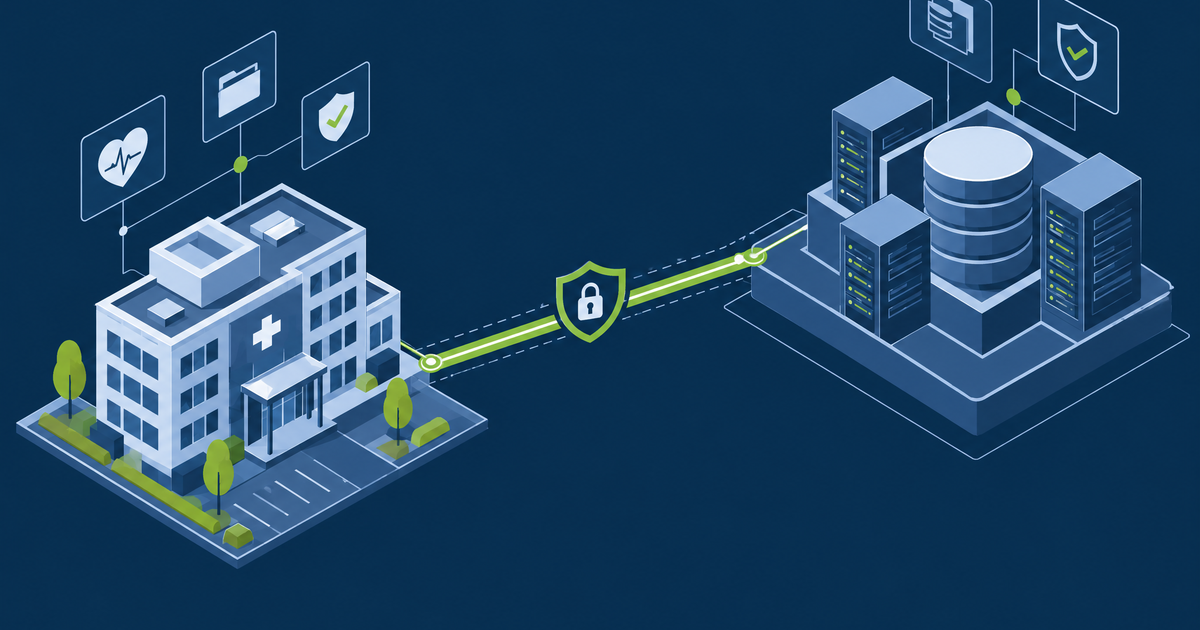
| Separate cloud tenancy | Cloud backup | Different identity domain is the control, not the location |
The distinction that catches people: governance mode versus compliance mode on object lock. Governance mode allows a sufficiently privileged user to remove the lock — which is exactly the user the attacker will become. Compliance mode does not. Choose compliance mode and accept that you also cannot delete early.
Retention against dwell time
Immutability only helps if the retention window is longer than the attacker's dwell time. If they were present for 60 days and your immutable window is 14, every surviving copy may already contain their foothold.
Verify it, because vendors describe this loosely
"Immutable" appears in a great deal of marketing. Test it:
- Log in as the highest-privileged account you have and attempt to delete a protected backup. It must fail.
- Attempt to shorten the retention period. It must fail.
- Attempt to delete the bucket, vault or container itself, not just an object.
- Check whether the backup software's own retention policy can expire it early.
- Confirm what happens when the subscription lapses — some providers release the lock.
Document the results. This is exactly the evidence an insurer or auditor will ask for, and it is the only way to know the control is real.
Where to start
Identify your most critical clinical system and establish one immutable copy with a 30-day minimum window and separate credentials. One system, done properly, is worth more than a plan covering everything that has not started.
Then prove you can restore from it — see backup testing, because an immutable copy you cannot restore is still not recovery.
GuardsArm assesses backup immutability and runs the deletion tests that show whether the control is genuine. Book a scoping call.
Written by GuardsArm Team
Our team of cybersecurity experts brings decades of combined experience in penetration testing, compliance auditing, and incident response. We're dedicated to helping organizations strengthen their security posture.
Take the next step on this topic
Talk to the GuardsArm team about how these services apply to your environment.