- SOC 2 Readiness
- 24/7 Security Monitoring
- Canadian-Based SOC
Software · SOC 2 readiness · Scoping brief
SOC 2 for a 14-person software company with no security team.
Enterprise customers had started asking for a SOC 2 report. The company wanted to know its gaps, the effort required from its own staff, and how far its existing tools could carry it.
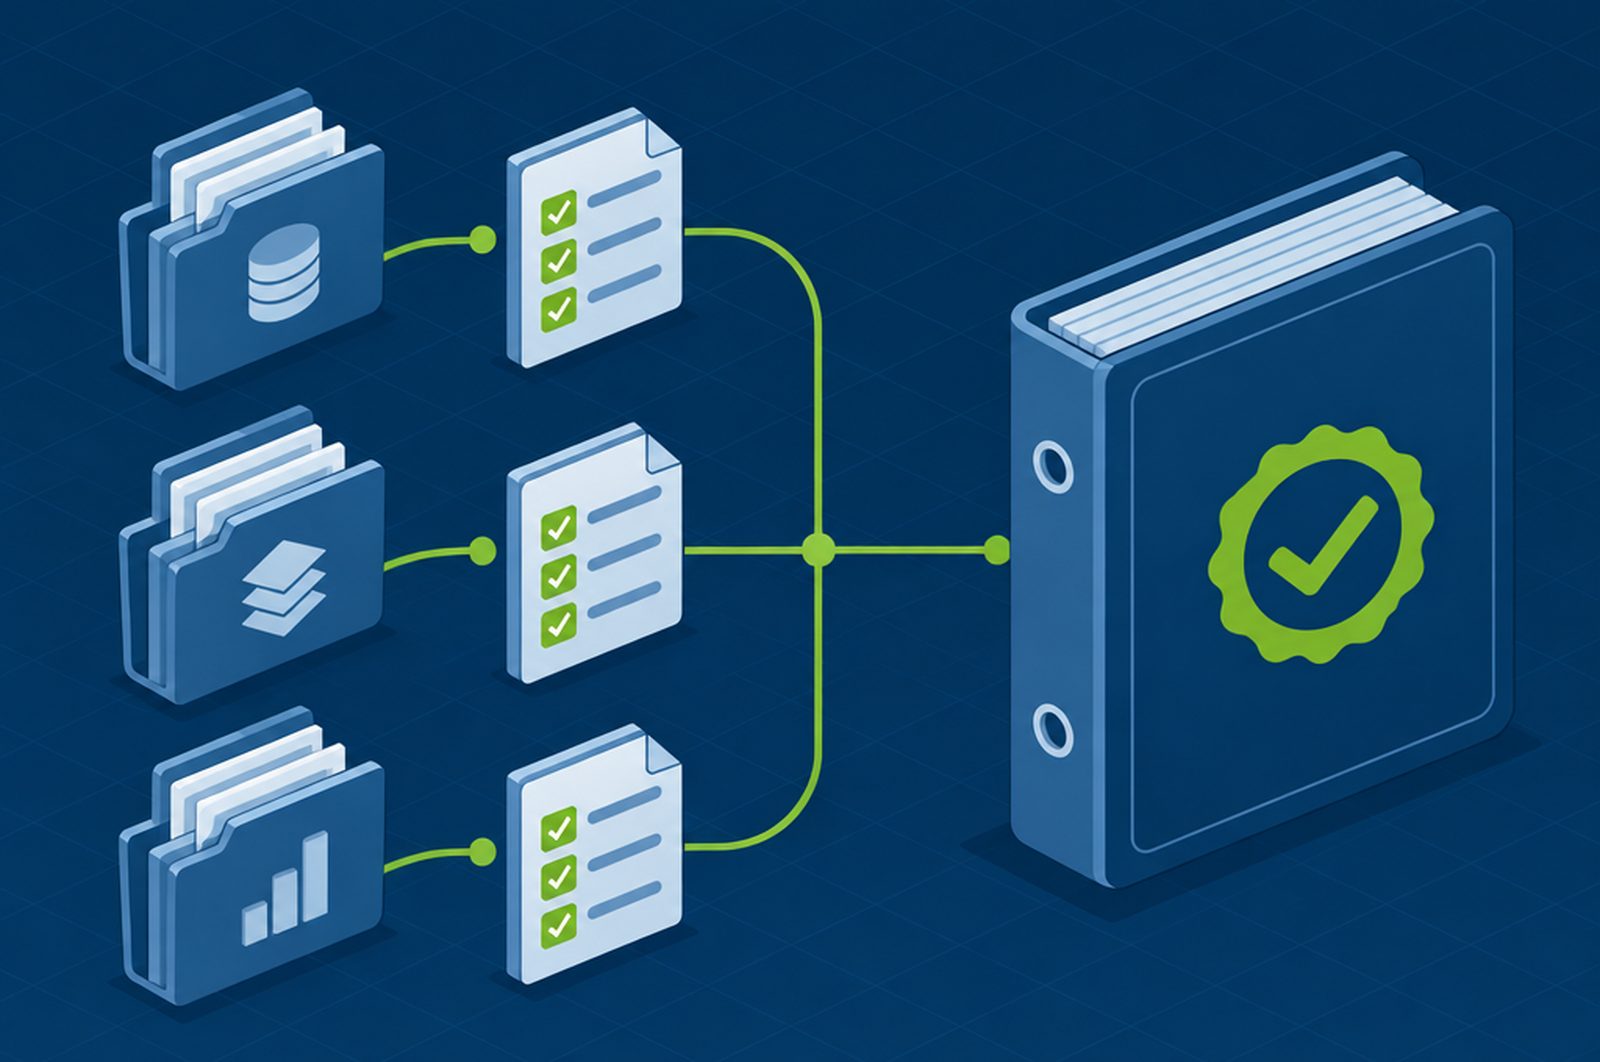
Scoping brief. This describes a problem a buyer brought to GuardsArm and how the engagement was scoped. It is not a record of delivered work, and no results are claimed. The organization is not named.
- Organization
- 14-person US environmental compliance software company
- Stage
- Scoping brief
- Sector
- Software
- Service
- SOC 2 readiness
The situation
Enterprise customers began asking for a SOC 2 report. The company had no dedicated security function.
It wanted to know the gaps, the effort required from its own people, and a practical roadmap using the Microsoft tools it already paid for.
How we scoped it
- A one-page engagement overview that answered the buyer's four questions directly
- A discovery questionnaire built around a Microsoft-based software vendor
- A three-phase fixed-fee program: readiness assessment, remediation, and audit support
- An optional 60-day monitoring pilot, so the team could see GuardsArm SIEM in its own environment first
- A clear line between GuardsArm’s work and the audit, which stays with an independent CPA firm
What a buyer in this position should ask any provider
- Does the quoted price take you to Type I or Type II?
- Are auditor fees included?
- How many hours will your own staff need to put in?
Planned deliverables
- Gap assessment
- Remediation roadmap
- Policy set
- Evidence preparation
- Auditor liaison
More from the record
Facing the same question?
Tell us what you need tested, monitored or evidenced. We will come back with a scope you can act on.
24/7 SOC Monitoring Available