
- SOC 2 Readiness
- 24/7 incident line
- 24/7 security operations team
Managed detection · Managed detection and response · Scoping brief
A buyer who asked for proof before pricing.
Scoping brief. How this engagement was scoped.
- Organization
- Prospective managed detection buyer
- Stage
- Scoping brief
- Sector
- Managed detection
- Service
- Managed detection and response
The situation
The buyer asked a direct question: when a system is compromised, can you show who, where, how and when?
They also wanted to see reporting as the incident happens.
How we approached it
- A live detection demonstration ran in a GuardsArm environment
- It showed the trail from first activity to an incident report
- Pricing was discussed only after the session, at the buyer’s request
- Scoping then opened with the buyer’s wider team
Planned deliverables
- Scoped monitoring proposal for the buyer’s environment
How GuardsArm runs managed detection
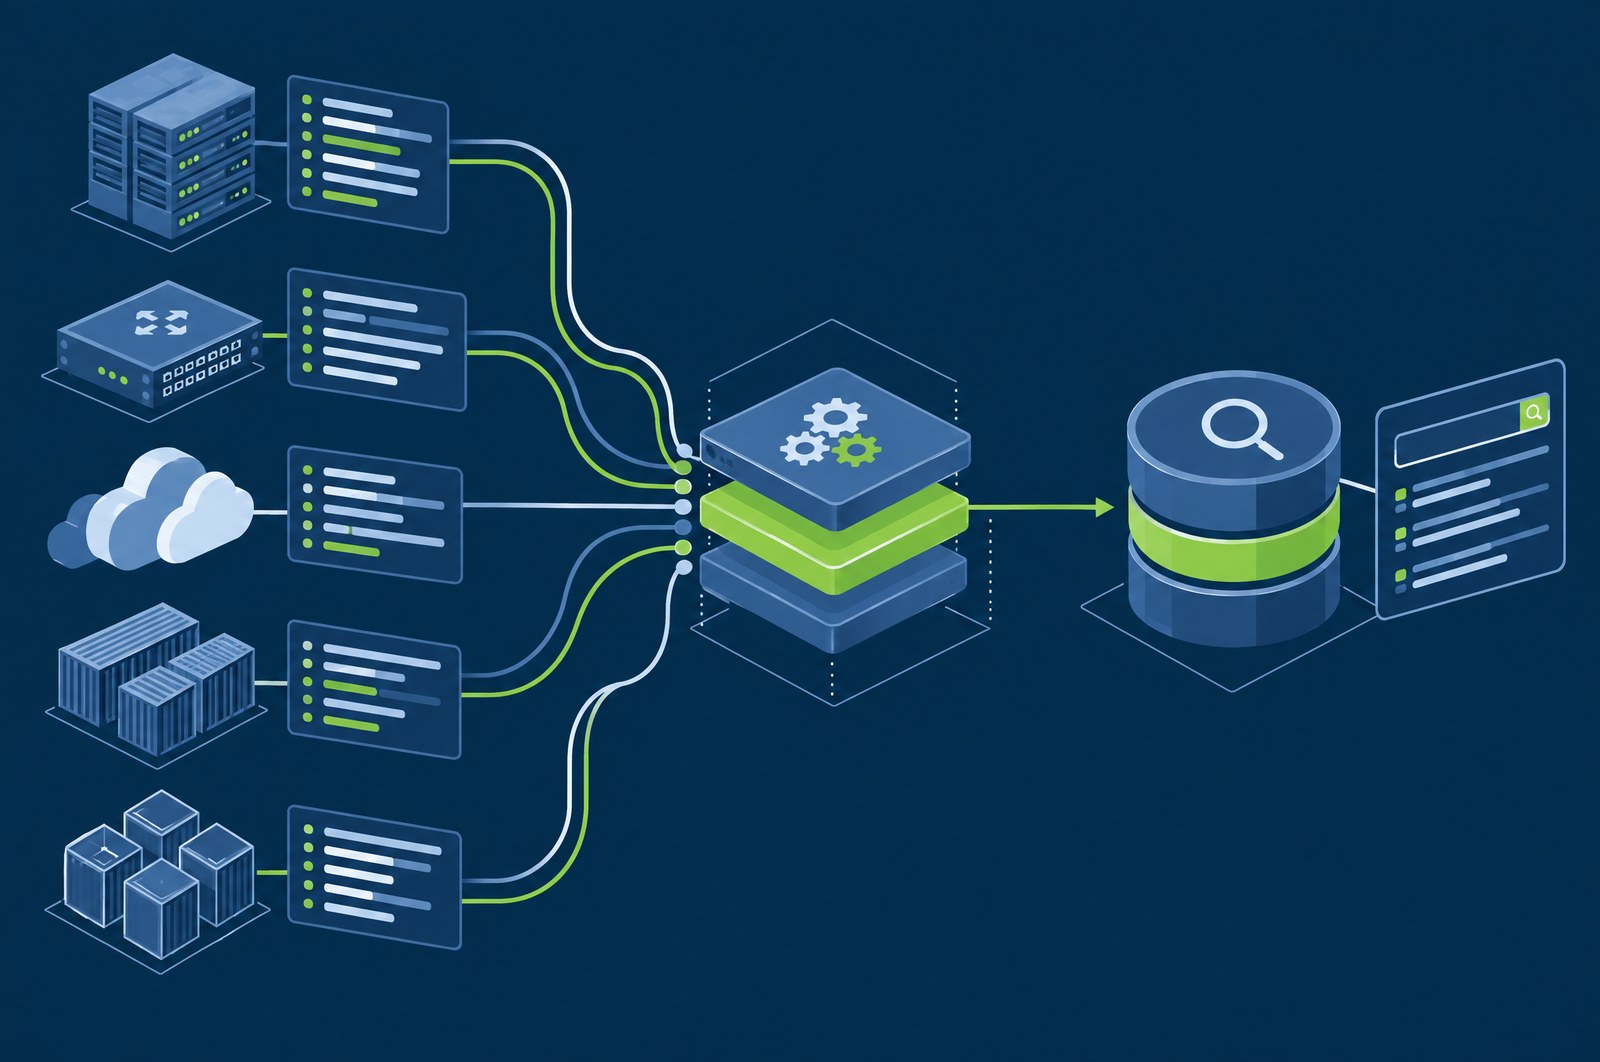
- Onboarding and log sourcesWe agree which endpoints, servers, cloud services and identity systems send telemetry, and confirm each source is arriving and parsed before it is counted as covered.
- Detection and correlationEvents from endpoints, identity, cloud and network sources are correlated and analysed continuously, with data kept in the location agreed with you.
- 24/7 triageAlerts are triaged by GuardsArm’s security operations centre around the clock, and escalated to your named contacts by severity.
- ResponseResponse actions are agreed in advance. Actions that change an endpoint require two people to approve them; read-only lookups run immediately.
- ReportingRegular security reports generated from the platform, written for the people who ask for proof: boards, regulators, insurers and auditors.
Standards we work to
- MITRE ATT&CK for detection coverage mapping
- NIST SP 800-61, Computer Security Incident Handling Guide
- Canadian Centre for Cyber Security baseline controls
Questions buyers ask
Where is our data stored?
GuardsArm’s SOC and platform keep security data in Canada.
Who operates the detection platform?
GuardsArm analysts do. The same team detects, investigates and contains threats around the clock.
Can you act on a threat, or only notify us?
That is agreed during onboarding. Pre-approved response actions can be taken by the SOC; anything that changes an endpoint needs two approvers.
Is there a minimum size?
GuardsArm’s pricing is calibrated for small and mid-sized organizations and municipalities as well as larger ones. Pricing is on consultation.
The service behind this work
SOC as a Service
Threats detected, investigated and contained around the clock.
Further reading
Threat Intelligence
Advanced Persistent Threats: Detection and ResponseThreat Intelligence
Advanced Threat Detection and Response StrategiesThreat Intelligence
Advanced Threat Intelligence for Proactive Security
Take it with you
Download this scoping brief as a PDF
The same account in a designed 5-page document, with how GuardsArm runs this kind of engagement and the questions buyers ask. Useful for sharing with your leadership or procurement team.
- Instant download
- A copy by email
- No spam